Microsoft & Cloud
Security Awareness Training Dubai Stop Phishing at the Human Layer
Your firewall does not open attachments. People do. Most successful breaches at Dubai businesses start with someone reasonable making a reasonable-looking mistake, and no amount of filtering closes that gap entirely. We run awareness training that treats staff as allies rather than suspects, because blame-based programmes teach people to hide mistakes instead of reporting them.
4.9★ · 645+ Google ReviewsSince 2007 · 19+ yearsTwo Dubai workshopsOpen Mon-Sat 9AM-7PM
Quick answer
- Main workshop
- Concord Tower, Media City
- Second office
- IT Center Building, Bur Dubai
- In Dubai since
- 2007
- Google rating
- 4.9 from 645 reviews
- Hours
- Mon-Sat 9AM-7PM
- Enquiries
- WhatsApp or use the quote form on this page
Why training beats filtering
Your firewall does not open attachments.
Filtering catches a great deal and will never catch everything. What gets through is by definition the message that looked legitimate, and at that point the control is a person making a reasonable judgement under time pressure. No amount of additional technology closes that gap.
How the training is run matters more than that it happens. Programmes built around blame teach staff to hide mistakes rather than report them, which is precisely backwards - the person who clicked and tells you within a minute is the most valuable security control you have.
Blame-based programmes teach people to hide clicks instead of reporting them.
People meet a harmless version first, which works far better than a briefing.
The employee who reports within a minute limits the damage more than any filter.
Repeat simulations show whether the training actually changed behaviour.
Why Technical Controls Are Not Enough
Spam filtering, MFA and endpoint protection all reduce risk. None of them close the gap where a person is persuaded to do something legitimate-looking.
- Filters catch known-bad patterns. Targeted phishing aimed at your finance team is written to look normal and often does
- Business email compromise usually involves no malware at all, so there is nothing for a scanner to detect
- Invoice fraud and supplier bank-change requests exploit process gaps, not software vulnerabilities
- MFA fatigue attacks work precisely because the technical control is present and the human is tired of it
- The realistic goal is not zero clicks. It is fast reporting when a click happens
Phishing Simulation, Run Fairly
Simulation is useful and easy to do badly. Done wrong, it damages trust and teaches staff that IT is a trap.
- Difficulty matched to the audience, escalating over time rather than opening with an unfair lure
- No simulations using bonuses, salary changes, redundancy or anything emotionally exploitative
- Results reported as team trends, not a leaderboard of named individuals
- Anyone who clicks gets a short explanation of the specific tells, delivered immediately and without blame
- Reporting a suspicious mail is celebrated, including when the mail turned out to be genuine
What the Reporting Should Tell You
Click rate alone is a vanity metric. The numbers that predict whether you survive a real attack are different.
- Report rate: how many people flagged it. This matters more than how many clicked
- Time to first report, which determines how quickly you can contain a real incident
- Repeat-click concentration, which shows whether risk sits with a few roles or across the business
- Trend over quarters rather than a single snapshot
- Departmental patterns, since finance and reception face different attacks and need different training
Making It Stick Beyond One Session
An annual session produces a spike and then decay. What changes behaviour is short, frequent and specific.
- Short reinforcement through the year rather than one long annual session
- Role-specific content: finance learns invoice fraud, reception learns pretexting, executives learn whaling
- A reporting button in Outlook or Gmail so flagging something takes one click
- Real incidents shared internally, anonymised, because a near-miss at your own company teaches more than any generic example
- Onboarding coverage, so new starters are not the weakest point by default
Why Azizi
Why Azizi Technologies for awareness training
We handle the incidents too, so the training reflects what actually happens to Dubai businesses rather than generic material.
No blame-based simulation
We do not name and shame, and we do not use cruel lures. Programmes that humiliate staff produce people who hide mistakes, which is the opposite of what you need.
Vendor-neutral
We are not reselling one platform. The programme is built around your business, and we will use whatever tooling you already own if it does the job.
We measure reporting, not just clicking
Report rate and time to report are what determine whether a real attack gets contained. Those are the numbers we put in front of management.
Our process
How we get started
Sequenced, scoped and shipped. Every phase has a deliverable you can hold us to.
- 01
Baseline where you are
An initial simulation and a short assessment, run before any training, so you can prove improvement later rather than assert it.
- 02
Agree the rules
What is in scope, what lures are off-limits, how results are reported and who sees them. Agreed with management before anything is sent.
- 03
Train by role
Short role-specific sessions rather than one generic deck. Finance, reception and leadership face genuinely different attacks.
- 04
Simulate and reinforce
Ongoing simulation at sensible intervals, with immediate coaching for anyone who clicks and recognition for anyone who reports.
Vendor neutral
Platforms We Support
Dubai businesses run mixed estates, so vendor loyalty is not useful here. These are the platforms we deploy and support day to day across both Dubai workshops.
- Microsoft 365 and AzureTenant administration, Intune device enrolment, Entra ID and conditional access, handled by Microsoft-certified engineers.
- Apple macOS fleetsThe default for creative and production teams. Managed alongside Windows under one contract.
- Cisco and ArubaSwitching, routing and enterprise WiFi for offices that outgrew consumer kit.
- Ubiquiti UniFiOur most common deployment for agency-sized offices. No per-AP licence and a strong controller.
- Sophos and FortinetFirewalls, EDR and MDR for teams that need security written into the AMC rather than bolted on.
- Synology and QNAPShared NAS over 10 GbE for editorial libraries, with backup that covers media rather than just documents.
Finding us
Office 45, Concord Tower
Our main workshop is Office 45 on the 10th floor of Concord Tower in Dubai Media City, with a second Azizi Technologies office at the IT Center Building in Bur Dubai. The nearest metro to Concord Tower is Dubai Internet City, and there is visitor parking (first 15 minutes free, then paid) if you drive.
No appointment is needed during workshop hours, Mon-Sat 9AM-7PM, Fri break 12-2PM · Sun closed. Remote support runs from both offices, and on-site visits are scheduled from whichever is closer to you.
Where we work on site
Dubai Media City, Internet City, Knowledge Park, Barsha Heights, Bur Dubai, Business Bay, JLT and the wider city from the two offices, with scheduled visits beyond Dubai.
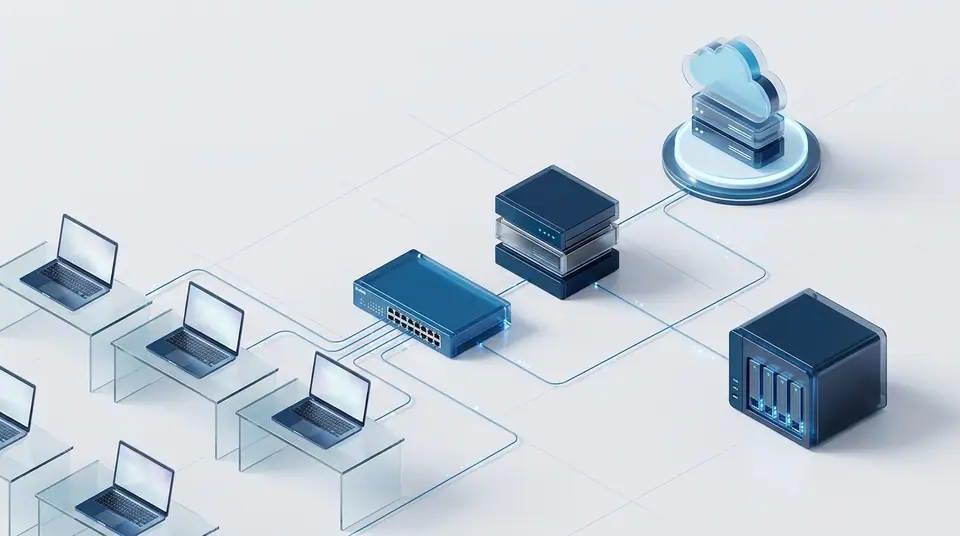
How engagements run
An assessment first, then a written scope with response times in the contract, then onboarding and ongoing support reviewed quarterly.
FAQ
Frequently asked questions
6 direct answers about Security Awareness Training Dubai.
Does security awareness training actually work?
Is phishing simulation unfair to staff?
How often should we run it?
What do we report to management?
Do we need this for compliance?
How many people can be in a session?
Explore more from Azizi Technologies
Official sources
Non-competitor sources we use for standards, platform rules and regulatory context.
An awareness programme built around your people
Next step
IT Support
Tell us your headcount and which teams handle payments or client data. We will baseline where you are today and quote a programme that fits.
Two Dubai offices, both walk-in
Concord Tower in Media City and the IT Center Building in Bur Dubai, Monday to Saturday 9:00 to 19:00.Find our offices
IT AMC Dubai: one written SLA for the whole estate
IT annual maintenance contracts with response times in the contract, for offices with or without in-house IT.IT AMC in DubaiGet a quote
Where do you want to start?
Four short steps, about a minute. Tell us the job once and we reply on WhatsApp with a price or a written scope, not a call-back.
4.9 stars from 645 Google reviews. Most enquiries answered within minutes during opening hours.
Read them on GoogleMeet the engineers
Real engineers. Real accountability.
Every job is handled by a certified engineer, the same people clients name in our Google reviews.
IT Support Lead
Usman K., thanked by name in our Google reviews
Microsoft Certified
10+ yrs experience
Senior Apple Repair Engineer
Shafeeq Ur Rehman, owner, on the Mac repair and micro-soldering bench
Apple-certified diagnostics · Board-level repair
12+ yrs experience
Network & Security Lead
Infrastructure and firewall team
Cisco CCNA
14+ yrs experience
Data Recovery Engineer
Drive imaging and board-level recovery bench
PC-3000 toolchain
9+ yrs experience
Finding us
Find your nearest Azizi Technologies office
Walk in to either Dubai branch, or book an assessment. Visitor parking at Concord Tower (first 15 minutes free, then paid) (Dubai Media City).
Dubai Media City
Concord Tower, Office 45, 10th floor
Dubai Media City, Dubai
Find us in Concord Tower, Dubai Media City. Visitor parking at Concord Tower (first 15 minutes free, then paid).
Opening hours:
Mon to Sat: 9:00 to 19:00, Friday break 12:00 to 14:00
Sun: closed
Bur Dubai
G 58, IT Center Building, 21 21A Street
Bur Dubai, Dubai
Find us on the ground floor of the IT Center Building, with the walk-in repair counter.
Opening hours:
Mon to Sat: 9:00 to 19:00, Friday break 12:00 to 14:00
Sun: closed
Azizi Technologies
The numbers behind the team
- Years in Dubai
- 19+
- Google Reviews
- 645+
- Vendor Certifications
- 3
- Dubai Workshops
- 2