IT Consulting & Projects
IT Compliance Consulting Dubai Meet the Standard, Provably
Compliance work goes wrong in two directions. Some businesses spend heavily chasing a standard nobody asked them for; others discover a requirement three weeks before a client audit. We start by establishing which standard genuinely applies to you, then assess the gap and fix it. We are the engineering side of compliance, not the certification body.
4.9★ · 645+ Google ReviewsSince 2007 · 19+ yearsTwo Dubai workshopsOpen Mon-Sat 9AM-7PM
Quick answer
- Main workshop
- Concord Tower, Media City
- Second office
- IT Center Building, Bur Dubai
- In Dubai since
- 2007
- Google rating
- 4.9 from 645 reviews
- Hours
- Mon-Sat 9AM-7PM
- Enquiries
- WhatsApp or use the quote form on this page
Where compliance goes wrong
Two opposite mistakes, both expensive.
Some businesses spend heavily chasing a standard nobody has actually asked them for, because it seemed prudent. Others discover a requirement three weeks before a client audit, when the options are bad and the price is whatever it costs. Both are failures of the same first step: nobody established which standard genuinely applies.
That is where we start. Then the gap assessment, then the engineering work to close it. We are the engineering side of compliance rather than the certification body, which means we have no incentive to tell you that you need more of it than you do.
Before any spending, because chasing the wrong one is the most common waste.
You see the distance before committing to the work.
No incentive to find you more requirements than you have.
Requirements met before a client asks, when options are still cheap.
Which Standards Apply to a UAE Business
This is the question worth answering first, because the cost of the whole programme depends on it. Several frameworks operate in the UAE and most businesses are subject to fewer than they fear.
- UAE PDPL, the federal personal data protection law, applies broadly to businesses handling personal data
- Sector rules can override: DIFC and ADGM operate their own data protection regimes for entities registered there
- ISO 27001 is not legally required but is frequently demanded contractually by enterprise and government clients
- PCI DSS applies if you store, process or transmit cardholder data, and its scope depends heavily on how you take payment
- Healthcare, government and critical infrastructure carry additional sector-specific requirements
- The honest starting point is usually a client contract or a tender, not a regulator
Gap Assessment
The assessment is where you find out how far you actually are, which is usually closer than expected on policy and further on evidence.
- Current state measured against the applicable standard, control by control
- Findings rated by effort and risk, so you can sequence rather than panic
- The distinction made clear between missing controls and controls that exist but are undocumented
- A realistic view of what can be fixed internally versus what needs external work
- Written so the board can read it, since compliance budget is approved by non-technical people
Evidence and Documentation
Most businesses fail audits on evidence rather than on security. The control exists, but nobody can prove it was operating.
- Policies written to match what you actually do, not downloaded templates describing a different company
- Evidence generated as a by-product of normal operations rather than assembled the week before an audit
- Access reviews, patch records, backup restore tests and training records retained on a schedule
- Asset and data inventories kept current, since these underpin almost every framework
- A clear owner for each control, because unowned controls decay
Staying Compliant After the Audit
Compliance is a state you maintain, not a project you finish. Most of the cost of a second audit is re-proving things that lapsed.
- A recurring calendar of reviews, tests and reports tied to the standard's requirements
- Change control, so new systems enter the scope deliberately rather than by accident
- Evidence collected continuously, which makes re-certification substantially cheaper than the first pass
- Periodic internal review ahead of the external one, so findings are not a surprise
Why Azizi
Why Azizi Technologies for compliance
We do the engineering half. Being clear about that boundary is more useful to you than pretending otherwise.
We are not a certification body
We do not issue certificates and we do not audit ourselves. Certification comes from an accredited body. We prepare you for it and fix what the assessment finds.
We can implement, not just report
Most compliance consultants hand you a findings document and leave. We are an IT company, so the remediation work is done by the same team.
We will tell you if a standard does not apply
Plenty of businesses are told they need ISO 27001 when a client actually asked for something far narrower. Establishing that early is the cheapest advice we give.
Our process
How we get started
Sequenced, scoped and shipped. Every phase has a deliverable you can hold us to.
- 01
Establish what applies
Your contracts, sector, jurisdiction and payment flows determine the standard. This step alone saves some clients an entire programme.
- 02
Gap assessment
Current state against the applicable controls, with findings rated by risk and effort and written for a business audience.
- 03
Remediate
We fix the technical gaps: access control, logging, backup, encryption, endpoint management, network segmentation.
- 04
Build the evidence trail
Policies matched to real practice, and evidence generated by normal operations rather than assembled retrospectively.
Vendor neutral
Platforms We Support
Dubai businesses run mixed estates, so vendor loyalty is not useful here. These are the platforms we deploy and support day to day across both Dubai workshops.
- Microsoft 365 and AzureTenant administration, Intune device enrolment, Entra ID and conditional access, handled by Microsoft-certified engineers.
- Apple macOS fleetsThe default for creative and production teams. Managed alongside Windows under one contract.
- Cisco and ArubaSwitching, routing and enterprise WiFi for offices that outgrew consumer kit.
- Ubiquiti UniFiOur most common deployment for agency-sized offices. No per-AP licence and a strong controller.
- Sophos and FortinetFirewalls, EDR and MDR for teams that need security written into the AMC rather than bolted on.
- Synology and QNAPShared NAS over 10 GbE for editorial libraries, with backup that covers media rather than just documents.
Finding us
Office 45, Concord Tower
Our main workshop is Office 45 on the 10th floor of Concord Tower in Dubai Media City, with a second Azizi Technologies office at the IT Center Building in Bur Dubai. The nearest metro to Concord Tower is Dubai Internet City, and there is visitor parking (first 15 minutes free, then paid) if you drive.
No appointment is needed during workshop hours, Mon-Sat 9AM-7PM, Fri break 12-2PM · Sun closed. Remote support runs from both offices, and on-site visits are scheduled from whichever is closer to you.
Where we work on site
Dubai Media City, Internet City, Knowledge Park, Barsha Heights, Bur Dubai, Business Bay, JLT and the wider city from the two offices, with scheduled visits beyond Dubai.
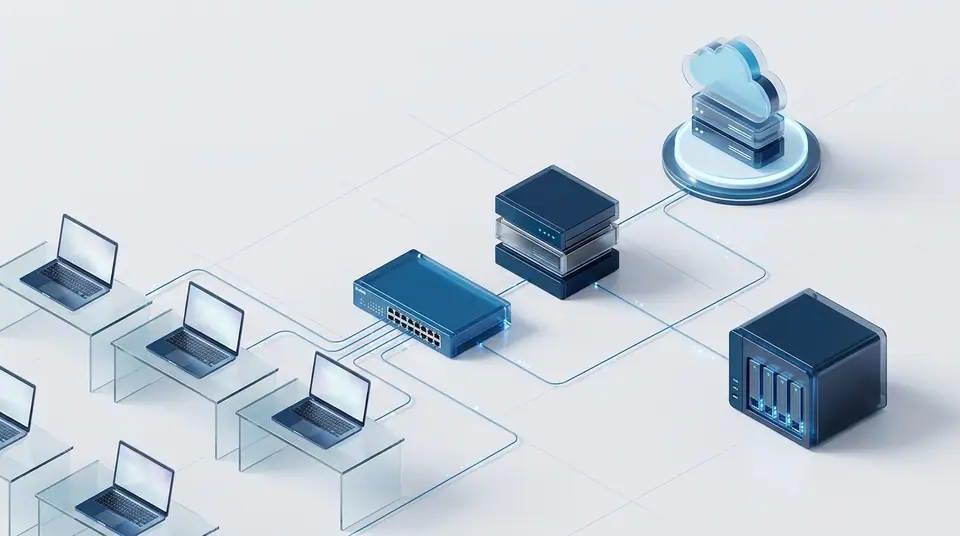
How engagements run
An assessment first, then a written scope with response times in the contract, then onboarding and ongoing support reviewed quarterly.
FAQ
Frequently asked questions
6 direct answers about IT Compliance Consulting Dubai.
Which compliance standard do we actually need?
Can you certify us to ISO 27001?
How long does ISO 27001 preparation take?
Do we need a consultant, or can we do it internally?
What evidence will an auditor ask for?
What drives the cost of a compliance programme?
Explore more from Azizi Technologies
Official sources
Non-competitor sources we use for standards, platform rules and regulatory context.
Find out which standard actually applies to you
Next step
IT Support
Tell us your sector, where you are registered and what your clients are asking for. We will confirm the applicable standard before quoting any programme.
Two Dubai offices, both walk-in
Concord Tower in Media City and the IT Center Building in Bur Dubai, Monday to Saturday 9:00 to 19:00.Find our officesIT AMC Dubai: one written SLA for the whole estate
IT annual maintenance contracts with response times in the contract, for offices with or without in-house IT.IT AMC in DubaiGet a quote
Where do you want to start?
Four short steps, about a minute. Tell us the job once and we reply on WhatsApp with a price or a written scope, not a call-back.
4.9 stars from 645 Google reviews. Most enquiries answered within minutes during opening hours.
Read them on GoogleMeet the engineers
Real engineers. Real accountability.
Every job is handled by a certified engineer, the same people clients name in our Google reviews.
IT Support Lead
Usman K., thanked by name in our Google reviews
Microsoft Certified
10+ yrs experience
Senior Apple Repair Engineer
Shafeeq Ur Rehman, owner, on the Mac repair and micro-soldering bench
Apple-certified diagnostics · Board-level repair
12+ yrs experience
Network & Security Lead
Infrastructure and firewall team
Cisco CCNA
14+ yrs experience
Data Recovery Engineer
Drive imaging and board-level recovery bench
PC-3000 toolchain
9+ yrs experience
Finding us
Find your nearest Azizi Technologies office
Walk in to either Dubai branch, or book an assessment. Visitor parking at Concord Tower (first 15 minutes free, then paid) (Dubai Media City).
Dubai Media City
Concord Tower, Office 45, 10th floor
Dubai Media City, Dubai
Find us in Concord Tower, Dubai Media City. Visitor parking at Concord Tower (first 15 minutes free, then paid).
Opening hours:
Mon to Sat: 9:00 to 19:00, Friday break 12:00 to 14:00
Sun: closed
Bur Dubai
G 58, IT Center Building, 21 21A Street
Bur Dubai, Dubai
Find us on the ground floor of the IT Center Building, with the walk-in repair counter.
Opening hours:
Mon to Sat: 9:00 to 19:00, Friday break 12:00 to 14:00
Sun: closed
Azizi Technologies
The numbers behind the team
- Years in Dubai
- 19+
- Google Reviews
- 645+
- Vendor Certifications
- 3
- Dubai Workshops
- 2