IT Consulting & Projects
Data Loss Prevention Dubai Stop Data Walking Out
Data rarely leaves a Dubai business through a dramatic breach. It leaves in a resignation month, attached to a personal email, or copied to a USB stick by someone who thought they were being helpful. DLP is about knowing what matters, controlling the routes out, and doing it without making everyone's job harder.
4.9★ · 645+ Google ReviewsSince 2007 · 19+ yearsTwo Dubai workshopsOpen Mon-Sat 9AM-7PM
Quick answer
- Main workshop
- Concord Tower, Media City
- Second office
- IT Center Building, Bur Dubai
- In Dubai since
- 2007
- Google rating
- 4.9 from 645 reviews
- Hours
- Mon-Sat 9AM-7PM
- Enquiries
- WhatsApp or use the quote form on this page
How data actually leaves
Not a dramatic breach. A resignation month.
The picture people have of data loss is an external attacker. The reality in most Dubai businesses is quieter and much more common: a client list forwarded to a personal email in someone's notice period, a project folder copied to a USB stick by somebody who genuinely thought they were being helpful, a file shared externally with a link that never expired.
DLP addresses that by knowing what actually matters, controlling the routes out, and doing it without making everyone's job harder - because controls that obstruct normal work get circumvented, which leaves you worse off than before.
Controls on everything is unworkable. Knowing what is sensitive is the starting point.
Personal email, removable media and external sharing links, not just the perimeter.
The window where most real data loss happens gets specific attention.
Controls people can work with, because ones they cannot get circumvented.
How Data Actually Leaves
Before buying a tool, it is worth knowing which routes matter for your business. They are rarely the ones people expect.
- Personal email: the most common route by far, usually during a notice period
- Cloud storage: a personal Drive or Dropbox account synced on a work laptop
- Removable media: USB drives and external disks, still common in design and engineering
- Screenshots and photos of a screen, which no technical control catches
- Over-shared links: a document set to anyone with the link and then forwarded onward
- Third parties: data sent to a supplier who has weaker controls than you do
Classification Before Control
This is the step that decides whether DLP works or becomes noise. You cannot protect everything equally, and trying to is how DLP gets switched off.
- Identify what genuinely matters: client data, contracts, payroll, source code, designs
- Classify by sensitivity, with a small number of labels rather than an elaborate scheme nobody applies
- Automatic classification where content patterns allow it, manual where judgement is needed
- Accept that most company data is not sensitive, and leave it alone
- Get owners to agree the classification, because IT guessing at business sensitivity produces bad policy
Policy Without Blocking Real Work
A DLP policy that stops people doing their job gets circumvented within a week, usually by routes you cannot see.
- Start in monitor-only mode to learn what normal looks like before enforcing anything
- Warn-and-justify before hard blocking, so users can proceed with a reason that gets logged
- Block outright only where the risk is genuinely severe, such as bulk client data to a personal address
- Tune against real false positives rather than shipping the vendor defaults
- Tell staff the policy exists and why, because covert monitoring damages trust when discovered
Monitoring and Incident Response
Detection without a response process is just a log nobody reads. Decide who acts and how before you turn anything on.
- Alerts routed to a named person with the authority to act, not a shared mailbox
- A defined process for what happens on a genuine incident, agreed with HR and management in advance
- Regular review of what is being flagged, so policy tightens or loosens based on evidence
- Evidence retained in a form usable for HR, insurers or a regulator
- Departure monitoring, since the notice period is the highest-risk window in most businesses
Why Azizi
Why Azizi Technologies for DLP
We have seen enough DLP deployments switched off after three months to know what causes that.
Monitor first, always
We will not enforce blocking on day one. Policies run in audit mode until we know what normal traffic looks like in your business.
Classification is a business decision
We facilitate it with your data owners rather than letting IT guess what is sensitive. Bad classification is the root of most DLP failure.
We plan the response, not just the alert
Alerts go to a named person with an agreed process. DLP that only produces logs is an expensive way to feel protected.
Our process
How we get started
Sequenced, scoped and shipped. Every phase has a deliverable you can hold us to.
- 01
Find and classify
What sensitive data you hold, where it lives and who owns it. Almost every client finds data in places nobody expected.
- 02
Map the exit routes
Which channels are actually in use, and which matter for your risk. This scopes the work realistically.
- 03
Monitor before enforcing
Policies run in audit mode first, so you learn what normal looks like and tune out false positives before anyone is blocked.
- 04
Enforce gradually
Warn first, block only where justified, starting with the highest-risk data and the clearest cases.
Vendor neutral
Platforms We Support
Dubai businesses run mixed estates, so vendor loyalty is not useful here. These are the platforms we deploy and support day to day across both Dubai workshops.
- Microsoft 365 and AzureTenant administration, Intune device enrolment, Entra ID and conditional access, handled by Microsoft-certified engineers.
- Apple macOS fleetsThe default for creative and production teams. Managed alongside Windows under one contract.
- Cisco and ArubaSwitching, routing and enterprise WiFi for offices that outgrew consumer kit.
- Ubiquiti UniFiOur most common deployment for agency-sized offices. No per-AP licence and a strong controller.
- Sophos and FortinetFirewalls, EDR and MDR for teams that need security written into the AMC rather than bolted on.
- Synology and QNAPShared NAS over 10 GbE for editorial libraries, with backup that covers media rather than just documents.
Finding us
Office 45, Concord Tower
Our main workshop is Office 45 on the 10th floor of Concord Tower in Dubai Media City, with a second Azizi Technologies office at the IT Center Building in Bur Dubai. The nearest metro to Concord Tower is Dubai Internet City, and there is visitor parking (first 15 minutes free, then paid) if you drive.
No appointment is needed during workshop hours, Mon-Sat 9AM-7PM, Fri break 12-2PM · Sun closed. Remote support runs from both offices, and on-site visits are scheduled from whichever is closer to you.
Where we work on site
Dubai Media City, Internet City, Knowledge Park, Barsha Heights, Bur Dubai, Business Bay, JLT and the wider city from the two offices, with scheduled visits beyond Dubai.
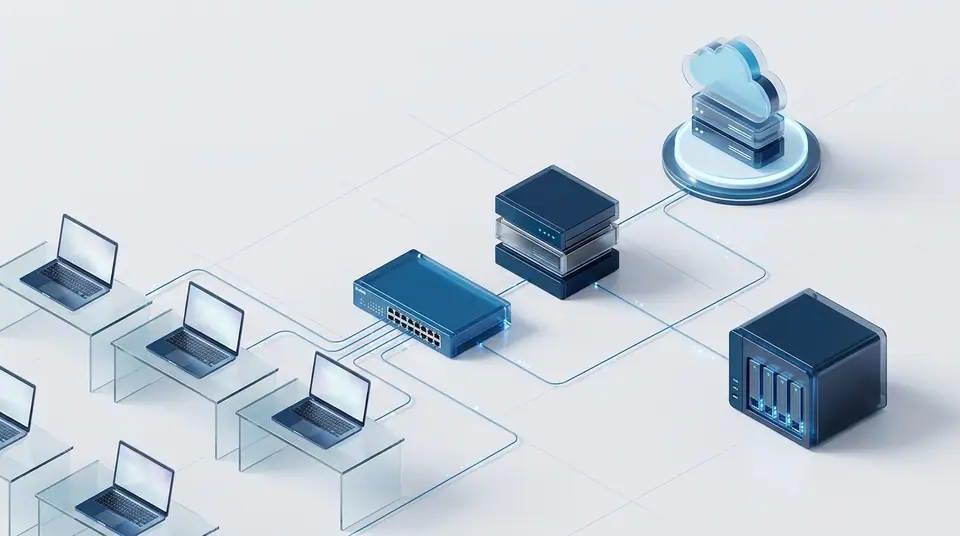
How engagements run
An assessment first, then a written scope with response times in the contract, then onboarding and ongoing support reviewed quarterly.
FAQ
Frequently asked questions
6 direct answers about Data Loss Prevention Dubai.
What does DLP actually catch?
Will we drown in false positives?
Which channel should we control first?
Is monitoring staff legal and fair?
Do we need a separate DLP product?
What happens when DLP flags something real?
Explore more from Azizi Technologies
Official sources
Non-competitor sources we use for standards, platform rules and regulatory context.
Find out where your data can walk out
Next step
IT Support
Tell us what kind of data you hold and how many staff handle it. We will map the exit routes and quote a monitor-first deployment.
Two Dubai offices, both walk-in
Concord Tower in Media City and the IT Center Building in Bur Dubai, Monday to Saturday 9:00 to 19:00.Find our offices
IT AMC Dubai: one written SLA for the whole estate
IT annual maintenance contracts with response times in the contract, for offices with or without in-house IT.IT AMC in DubaiGet a quote
Where do you want to start?
Four short steps, about a minute. Tell us the job once and we reply on WhatsApp with a price or a written scope, not a call-back.
4.9 stars from 645 Google reviews. Most enquiries answered within minutes during opening hours.
Read them on GoogleMeet the engineers
Real engineers. Real accountability.
Every job is handled by a certified engineer, the same people clients name in our Google reviews.
IT Support Lead
Usman K., thanked by name in our Google reviews
Microsoft Certified
10+ yrs experience
Senior Apple Repair Engineer
Shafeeq Ur Rehman, owner, on the Mac repair and micro-soldering bench
Apple-certified diagnostics · Board-level repair
12+ yrs experience
Network & Security Lead
Infrastructure and firewall team
Cisco CCNA
14+ yrs experience
Data Recovery Engineer
Drive imaging and board-level recovery bench
PC-3000 toolchain
9+ yrs experience
Finding us
Find your nearest Azizi Technologies office
Walk in to either Dubai branch, or book an assessment. Visitor parking at Concord Tower (first 15 minutes free, then paid) (Dubai Media City).
Dubai Media City
Concord Tower, Office 45, 10th floor
Dubai Media City, Dubai
Find us in Concord Tower, Dubai Media City. Visitor parking at Concord Tower (first 15 minutes free, then paid).
Opening hours:
Mon to Sat: 9:00 to 19:00, Friday break 12:00 to 14:00
Sun: closed
Bur Dubai
G 58, IT Center Building, 21 21A Street
Bur Dubai, Dubai
Find us on the ground floor of the IT Center Building, with the walk-in repair counter.
Opening hours:
Mon to Sat: 9:00 to 19:00, Friday break 12:00 to 14:00
Sun: closed
Azizi Technologies
The numbers behind the team
- Years in Dubai
- 19+
- Google Reviews
- 645+
- Vendor Certifications
- 3
- Dubai Workshops
- 2