VPN setup for small businesses in Dubai went through three phases: pre-COVID corporate VPN was rare; 2020-2023 every SMB rushed to deploy OpenVPN or basic site-to-site; 2024-2026 the shift to zero-trust network access (ZTNA). Here's the practical 2026 guide for Dubai SMBs - what kind of VPN you actually need, vendor choices, real AED budgets, and install steps.
Three types of VPN every Dubai SMB should know
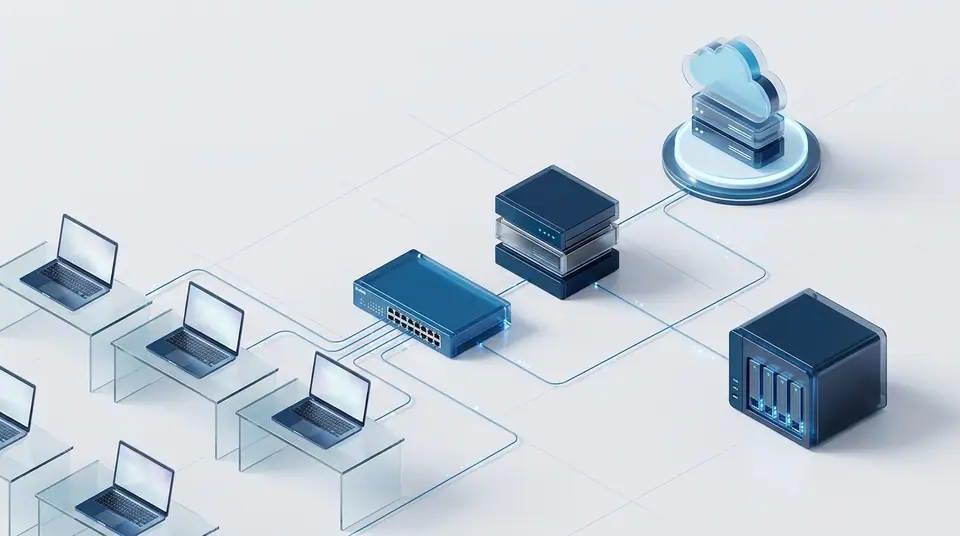
Every Dubai SMB VPN need falls into one of three patterns - site-to-site, client-to-site, or zero-trust network access. (1) Site-to-site VPN: connects two physical offices (e.g. Dubai HQ to Sharjah branch, or to AWS Middle East Bahrain). Built on the firewall, always-on, transparent to users. (2) Client-to-site VPN: individual user devices (laptops, phones) connect to the office network from home or travel. Most common SMB use case. (3) Zero-trust network access (ZTNA): per-application access rather than full network access. The future direction - reduces blast radius if a single device is compromised.
Do you actually need a VPN in 2026?
Three concrete tests. (1) Do you have an on-premise file server or app that staff need to access remotely? Yes - need client-to-site VPN. (2) Do you have multiple Dubai or GCC offices that need to share internal resources? Yes - need site-to-site VPN. (3) Are you a cloud-only office (Microsoft 365, Google Workspace, all SaaS, no on-prem servers)? You probably don't need a VPN - identity-based access with MFA is sufficient. Lots of Dubai SMBs deploy VPN out of habit when they don't actually need one.
The 60-second scoping question
Count the systems that physically live in your office. If the answer is zero - no file server, no NAS, no ERP box, no CCTV recorder you need to reach remotely - you probably need identity-based access with MFA, not a VPN. That one question stops many Dubai SMBs buying firewall hardware they do not need.
Is a business VPN legal in the UAE?
Yes - VPNs for legitimate business use are legal, routine and standard practice in the UAE; what the law penalises is using a VPN to commit an offence, not the technology itself. Site-to-site links between your offices, remote staff reaching an office file server, encrypted access to your own cloud servers, and fixed-IP connectivity for ERP or payment systems are all normal corporate use, and banks and free-zone companies across Dubai run them. Two practical guardrails for SMB owners: run the VPN on business-grade infrastructure under your trade licence (a FortiGate or UniFi gateway on a business internet plan, not a consumer privacy app), and issue a one-page acceptable-use policy so staff know company VPN access exists for work systems.
Vendor options for small business VPN
| Solution | Best For | Hardware AED | Annual AED |
|---|---|---|---|
| FortiGate 60F (built-in SSL VPN) | 10-50 user SMB | AED 3,500 | AED 1,200 licence |
| Cisco Meraki MX67 (Client VPN) | 10-50 user, audit-heavy | AED 6,500 | AED 2,500 licence |
| pfSense / OPNsense (free) | Tech-savvy 5-30 users | AED 1,500 mini PC | AED 0 |
| Ubiquiti UDM Pro (WireGuard) | Up to 50 users | AED 1,800 | AED 0 |
| Cloudflare Zero Trust | Modern ZTNA, cloud-first | AED 0 | AED 250-500/user/year |
| Tailscale (mesh VPN) | Distributed teams 5-100 | AED 0 | AED 200-400/user/year |
VPN options for Dubai SMBs (2026)
WireGuard, IPsec, OpenVPN or SSL VPN - which protocol should you pick?
Default to WireGuard for client-to-site (staff laptops to the office), IPsec IKEv2 for site-to-site between firewalls, and your firewall's SSL VPN only where it's already licensed - OpenVPN is the legacy choice for new 2026 deployments. WireGuard is a small modern codebase (around 4,000 lines), connects in under a second, and survives the hop from office WiFi to mobile data without dropping - which is why UniFi gateways, pfSense and Tailscale standardised on it. IPsec remains the interoperability standard: a FortiGate in Dubai will hold a stable tunnel to a Meraki MX or an AWS gateway for years. SSL VPN portals are convenient because they bundle MFA and per-user policy - but they face the open internet and must be patched fast.
| Protocol | Best for | Notes |
|---|---|---|
| WireGuard | Client-to-site, mesh overlays (Tailscale) | Fastest and simplest; UDP 51820; built into UDM Pro and pfSense |
| IPsec IKEv2 | Site-to-site, firewall-to-cloud | Vendor-neutral standard; UDP 500/4500 |
| SSL VPN (FortiGate/Meraki) | Client-to-site with MFA portal | Easy rollout; internet-facing, patch promptly |
| OpenVPN | Existing installs only | Mature but slower; legacy for new builds |
VPN protocol choice for Dubai SMBs (2026)
Throughput is rarely the deciding factor: a AED 1,800 UDM Pro or a AED 3,500 FortiGate 60F (typical Dubai retail) pushes several hundred megabits through a tunnel - more than the uplink most Dubai SMBs run. Choose on manageability and patching, not raw speed.
Recommended setup by Dubai SMB profile
- 5-15 user cloud-only office: skip traditional VPN, use Cloudflare Zero Trust or Tailscale for selective access
- 10-30 user office with on-prem file server: FortiGate 60F or Ubiquiti UDM Pro with client-to-site SSL VPN, quoted on user count and site survey
- 20-50 user office with two Dubai branches: FortiGate 60F or 80F at each site for site-to-site IPsec VPN, quoted per site
- DIFC / ADGM regulated SMB: Cisco Meraki MX67 or MX95 for audit trail, quoted after a compliance scoping call
- Tech startup with engineers needing per-app access: Tailscale or Cloudflare Zero Trust, a per-user vendor subscription, no hardware
- Office with travelling sales team: client-to-site SSL VPN on FortiGate or Meraki, plus mobile clients (FortiClient, AnyConnect)
Which Etisalat and du settings break business VPNs?
Three ISP-side details break more Dubai VPN installs than any firewall bug: double NAT from the ISP router, a missing static IP, and unforwarded ports. Fix them in this order before debugging anything else:
- 1Put the Etisalat or du modem in bridge mode (call 101 or 155 to request it) so your FortiGate or UDM Pro holds the public IP - a VPN endpoint behind double NAT drops inbound connections unpredictably.
- 2Order a static IP on your business plan - a standard add-on on Etisalat Business and du business tariffs. Without it, your endpoint address changes after every outage and all remote clients and site-to-site peers go down until reconfigured; dynamic DNS is an acceptable fallback for client-to-site only.
- 3Forward only the ports your protocol needs: UDP 51820 for WireGuard, UDP 500 and 4500 for IPsec, and your chosen HTTPS port (such as 10443) for FortiGate SSL VPN - nothing else.
- 4Re-check bridge mode after any ISP plan change or router swap - field technicians routinely reset boxes to routed mode, and the VPN mysteriously dies a day later.
Install steps for FortiGate client-to-site VPN
Standard Azizi Technologies install guide for a 25-user Dubai SMB with FortiGate 60F: (1) order FortiGate 60F plus 25-user SSL VPN licence (roughly AED 4,700 at Dubai retail for hardware plus licence). (2) Connect to Etisalat or du modem in bridge mode. (3) Configure SSL VPN portal at https://office.example.com:10443 with custom branding. (4) Set up FortiToken MFA for every user (mandatory). (5) Create AD or local user database with per-user permissions (HR can access HR shares, finance can access finance shares, etc). (6) Install FortiClient on each user laptop and phone, pre-configured. (7) Test from outside the office. Total install time: 1 working day. Installation is quoted separately from the hardware, after a site survey.
An unpatched VPN portal is worse than no VPN
Internet-facing SSL VPN portals are the most-attacked service on SMB firewalls - multiple FortiOS SSL VPN vulnerabilities have been mass-exploited in recent years, usually months after a patch was already available. Whoever owns your firewall must apply firmware updates within days of release, or the VPN itself becomes the way in. Azizi Technologies includes firmware patching and configuration backups in its network AMC plans.
Want the firewall and VPN handled end to end?
We supply, configure and patch FortiGate and UniFi gateways for Dubai SMBs - VPN, MFA and monitoring included, with a site survey first.
Can you run a site-to-site VPN to AWS or Azure from Dubai?
Yes - a standard IPsec tunnel from your office FortiGate or UDM Pro to AWS me-central-1 (UAE) or Azure UAE North gives the office a private route to your cloud servers, with single-digit-millisecond latency from Dubai. The cloud side is a managed VPN gateway (AWS Site-to-Site VPN costs about USD 0.05 per connection-hour, roughly AED 135 a month, plus data transfer; Azure VPN Gateway is similar by tier), so there is no second firewall to buy. The office side needs the static IP and bridge mode described above. For a 10-30 user SMB moving its file server to the cloud, this is a half-day configuration job, not a project.
Data residency note for regulated firms
DIFC and ADGM data protection rules, and many UAE government contracts, expect client data to stay in-country. AWS me-central-1 and Azure UAE North are physically in the UAE - which is why a site-to-site tunnel to a local region, not a European one, is the default architecture for regulated Dubai SMBs.
Why zero-trust is the future direction
Traditional VPN gives full network access once authenticated - a compromised laptop with VPN credentials becomes a compromised network. Zero-trust network access (ZTNA) flips this: every application access decision is made per-request based on user identity, device posture, and context. Cloudflare Zero Trust, Zscaler, Netskope and Palo Alto Prisma Access are the vendors we see most often. For new Dubai SMBs setting up VPN in 2026, ZTNA is recommended over legacy VPN. Existing VPN setups don't need urgent migration - plan ZTNA migration during next firewall refresh.
The MFA rule that stops most VPN break-ins
Every VPN account, every administrator, every privileged access must have MFA enforced - not optional, not recommended. Use FortiToken, Cisco Duo, Microsoft Authenticator, or YubiKey hardware tokens. SMS-based MFA is now considered weak. Authenticator apps are free and hardware tokens are a small one-time cost per user, and MFA blocks the most common Dubai SMB breach vector (credential stuffing on VPN portals).
Which VPN mistakes cause the most Dubai SMB breaches?
The same six mistakes account for nearly every VPN-related incident we get called in to clean up - and all six are cheap to fix:
- No MFA on the VPN portal - credential-stuffing bots find Dubai SSL VPN portals within days of going live
- One shared VPN account for the whole team - no way to revoke a leaver or trace actions; create per-user accounts
- Full-network access for everyone - the accountant's laptop does not need to reach the CCTV VLAN; scope access per group
- Firewall firmware never updated after install day - schedule quarterly updates or put it on an AMC
- No logging - connection logs are the difference between a 1-hour and a 1-week investigation; enable them and retain 90 days
- Setup done by a long-gone employee with no documentation - keep admin credentials and a config backup where the owner controls them
"Most small offices in Dubai do not need a complicated VPN. They need one firewall, bridge mode, a static IP, MFA on every account, and someone who actually patches the box. That five-item list prevents almost everything we get called in to fix."
Dubai SMB VPN setup consultation
Send your office address, staff count, and your specific remote-access need (on-prem files, multi-branch, travelling team). We'll recommend the right VPN architecture and quote the total cost in writing.